Answered: [Security threat] tags are not sanitized in extra question field

Post date: 2020-07-01 00:44:51
Views: 419

Hey q2apro, I think you are testing the default q_view_extra($q_view); function.

The default function is still safe. But if you pull the content from the databse, it's not safe.

First, look! The script is stored in database.

database

Second, if create a function to pull that content form the datase:

public function q_item_extra($q_item)
{
$postidz = $q_item'raw']'postid'];
$extra = qa_db_read_one_value(qa_db_query_sub(
       'SELECT content FROM ^postmetas WHERE title="qa_q_extra" AND postid=#',
        $postidz
   ), true);
 
 //$extra = $q_item'extra']'content'];
 
        $this->output('My info:'.$extra);   
   
}

Here's the result:
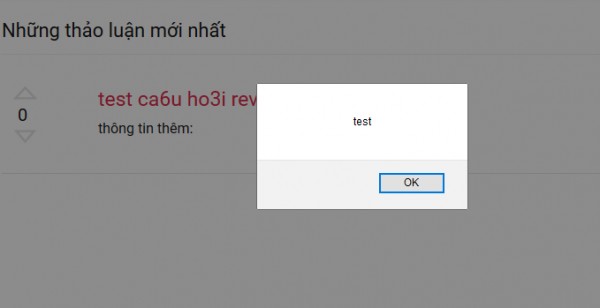
test

I hope you'll get my point.

Please click Here to read the full story.
 
Other Top and Latest Questions:
This water technology stock is set to get a big boost from AI, says Wells Fargo
Russian crude production rebounds after Trump diesel deal, IEA says as oil markets return to surplus
This cybersecurity stock is down nearly 20% over the past month. KeyBanc says it's a buy
Cisco beats on earnings, says AI infrastructure revenue will double this fiscal year
Black Market White Milk
sports podcasts (especially North American sports: MLB, NHL, NBA)
Big scary medical bill
The Lord of the Rings: The Rings of Power: Marnûkh
Movie: Linda Linda Linda
‘We will sue them’: Canada threatens Stellantis as Trump trade war reshapes Jeep production plans